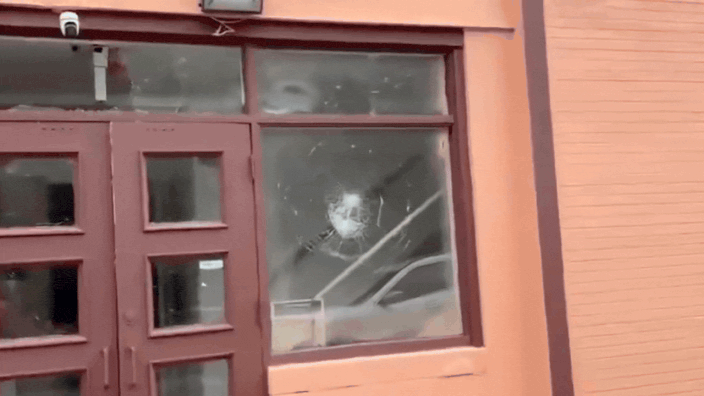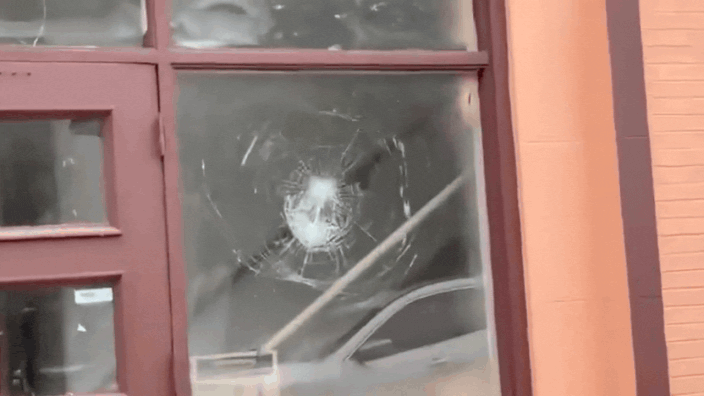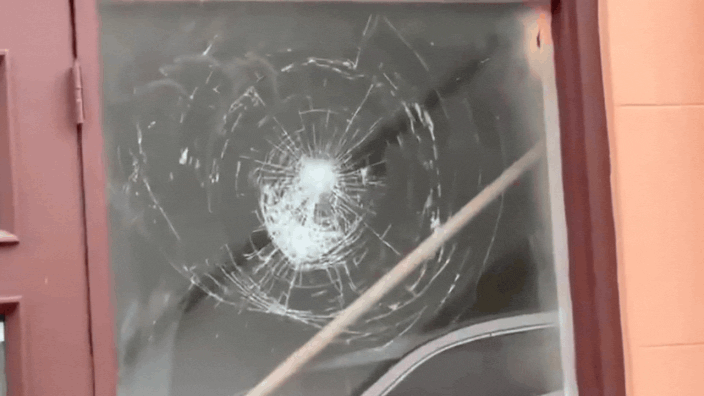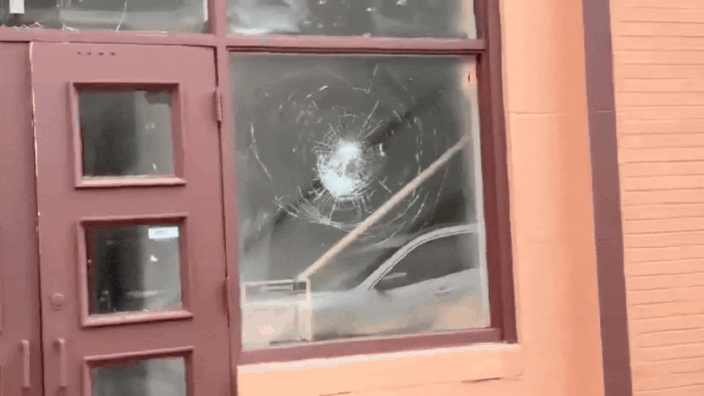
When a house of worship suffers physical damage, public discourse typically fragments into polarized outrage or procedural platitudes. However, analyzing such incidents through a structural lens reveals predictable vulnerabilities in localized security architecture rather than isolated anomalies. Vandalism targeting religious infrastructure operates within an economic and logistical framework that can be systematically deconstructed, measured, and mitigated.
The Cost Function of Religious Facility Vulnerability
Securing open-access community spaces involves an inherent tension between public hospitality and asset protection. Places of worship are architecturally optimized for open congregation, which introduces significant perimeter exposure. Discover more on a connected topic: this related article.
The security deficit of religious properties can be modeled through a simple risk equation where total vulnerability equals exposure multiplied by accessibility, divided by active deterrence.
When an institution prioritizes unrestricted public access to minimize social friction, exposure increases exponentially. If surveillance coverage, illumination, and physical barriers remain static, the overall vulnerability index rises. Vandalized properties frequently share common structural failure points: More journalism by USA Today highlights similar views on the subject.
- Perimeter permeability: Absence of setback architecture or physical zoning that separates pedestrian walkways from structural walls.
- Surveillance asymmetry: Static or outdated camera placements that capture evidentiary footage post-incident but provide zero active deterrence or real-time intervention capability.
- Response latency: The time delta between a breach occurrence and law enforcement arrival, which consistently exceeds the duration required to execute property damage.
The Escalation Dynamic and Institutional Response
When a physical assault on a facility occurs, community stakeholders and representative organizations invariably issue demands for swift administrative and legal action. While political accountability and law enforcement prioritization serve immediate deterrent functions, they represent lagging indicators of security health.
The mechanics of community reaction follow a distinct cycle:
- Incident occurrence: Physical disruption of the perimeter and subsequent property damage.
- Narrative mobilization: Rapid dissemination of the event through digital networks, amplifying community anxiety.
- Policy friction: Demands for increased protection clashing with municipal zoning laws, budget constraints, and architectural limitations.
- Temporary hardening: Short-term deployment of patrols or temporary lighting, followed by regression to baseline vulnerabilities as public attention shifts.
This cycle highlights a systemic failure to treat security as a continuous engineering problem. Relying on post-incident deterrence strategies guarantees recurring vulnerability because it addresses the symptom rather than the systemic exposure gradient.
Engineering a Resilient Defense Framework
Transitioning from reactive outrage to structural resilience requires an operational shift in how community assets are managed. This involves three distinct structural pillars.
First, perimeter hardening must be decoupled from aesthetic openness through the integration of invisible defense mechanisms. CPTED (Crime Prevention Through Environmental Design) principles demonstrate that natural surveillance, territorial reinforcement, and access control can be embedded into landscaping and structural design without compromising the welcoming ethos of a facility. Replacing ornamental, easily breached boundaries with reinforced architectural landscaping alters the kinetic effort required for vandalism.
Second, monitoring systems must transition from passive recording to active detection. Modern optical sensors integrated with edge-computing analytics can identify loitering, thermal anomalies, or unauthorized perimeter crossings during high-risk windows, triggering automated lighting or localized alerts before physical contact with the structure occurs.
Third, institutional resource pooling must replace isolated facility management. Individual religious sites often lack the capital expenditure budgets required to maintain enterprise-grade security infrastructure. Centralized security syndicates that aggregate risk data, share intelligence on local threat vectors, and coordinate rapid response protocols across multiple institutions reduce the per-unit cost of comprehensive defense while eliminating single points of failure.
Mitigating physical threats against community infrastructure demands an abandonment of purely emotional responses in favor of rigorous risk management, asset auditing, and architectural adaptation. Security is not a static policy statement; it is an ongoing economic and logistical allocation of resources against predictable failure points.