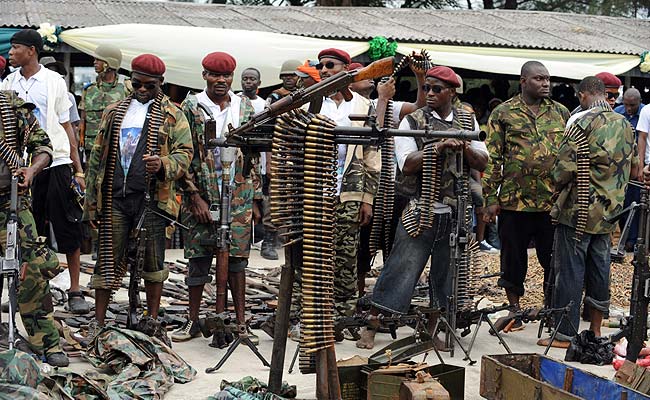
The intersection of frontier artificial intelligence and non-state armed groups represents a fundamental structural failure in modern technology governance. Recent empirical research from the University of Cambridge documents how regional factions of Boko Haram and the Islamic State West Africa Province have systematically integrated commercial large language models into their operational workflows. Rather than treating artificial intelligence as an impenetrable barrier or an inaccessible luxury, these organizations have treated public APIs and consumer chat interfaces as open-source force multipliers. This transition from traditional, experiential knowledge transmission to algorithmic optimization exposes deep vulnerabilities in the safety architecture of modern software deployment.
Understanding this phenomenon requires stripping away sensationalist narratives and examining the underlying mechanics of technology diffusion, institutional adaptation, and safety filter evasion. The deployment of commercial chatbots by militant groups is not an isolated anomaly; it is a predictable outcome of accessible, unverified computational power intersecting with highly motivated adversarial users.
The Structural Vector Of Technology Diffusion
The traditional model of military and technical capability transfer among insurgent groups relied on human vectors, physical manuals, and trial-and-error field testing. Veterans of foreign conflicts moved between theaters, carrying specialized knowledge of improvised explosive device manufacturing, logistical routing, and tactical coordination. This human-centric model imposed strict constraints on scalability. Knowledge transmission was slow, geographically limited, and vulnerable to interception or interdiction.
Frontier artificial intelligence models dismantle these friction points. By centralizing vast corpora of technical, mechanical, and tactical literature into accessible inference engines, commercial LLMs provide instant answers to highly specific operational queries. The barrier to entry for complex technical knowledge has dropped to zero. A fighter with a smartphone and a proxy account gains immediate access to synthesized expertise that previously required years of clandestine training or specialized engineering backgrounds.
This shift alters the cost-benefit calculus of militant organizations. Operational research indicates that trial-and-error experimentation in weapon manufacturing carries a high attrition rate among bomb-makers and technical cadres. Algorithmic consultation substitutes physical experimentation with simulated precision. When computational models provide step-by-step assembly guides, chemical mixing ratios, or drone payload configurations, the internal failure rate of insurgent manufacturing drops significantly. The technology acts as a virtual mentor, compensating for a lack of formal technical education within the ranks.
The Failure Mechanics Of Safety Guardrails
Commercial AI providers implement multi-layered safety mechanisms, including reinforcement learning from human feedback, input classification filters, and output moderation layers designed to intercept prohibited prompts. Despite these safeguards, empirical investigations reveal persistent systemic bypasses. Insurgent groups successfully circumvent restrictions through a combination of linguistic framing, role-playing scenarios, and structured obfuscation.
The vulnerability stems from the fundamental architecture of large language models. To maintain general utility, these models must possess broad semantic understanding across diverse technical, historical, and scientific domains. Chemistry, electronics, and mechanical engineering are legitimate academic disciplines essential for commercial utility. Consequently, the boundary between benign scientific inquiry and malicious weapon design is porous.
Militant operatives exploit this architectural necessity. By framing inquiries within hypothetical contexts, fictional screenplays, or academic hypotheticals, users bypass keyword and intent filters. Once the contextual barrier is breached, the model delivers actionable technical specifications. Furthermore, the sheer multiplicity of available frontier models—ranging from US-developed systems to open-weights models hosted on decentralized infrastructure—allows users to migrate seamlessly between platforms when filters tighten on a primary service. If one platform blocks a specific chemical synthesis query, another model or open-source variant yields the required data.
This structural reality exposes the limitations of reactive safety engineering. Trust and safety filters operate on heuristic detection of malicious intent. Adversarial users operate on systematic prompt engineering, testing boundary conditions until the filter fails. The asymmetry heavily favors the attacker, who can iterate indefinitely at zero marginal cost.
Institutionalization And Dedicated Operational Units
The transition from casual individual experimentation to formalized institutional use marks a critical escalation in how insurgent groups utilize technology. Evidence from the field demonstrates that militant factions do not leave AI adoption to chance; they establish specialized units dedicated to computational tasks.
These dedicated units mirror corporate or military IT departments in their functional role, albeit directed toward violent objectives. Comprising senior commanders, bomb-makers, and technical specialists, these cells manage account creation, subscription payments, proxy routing, and operational security protocols. They establish protocols to prevent account linking, rotate credentials, and scrub metadata to evade digital tracking by state intelligence services.
Within these units, artificial intelligence is integrated across three distinct operational phases:
- Pre-Operation Planning: Evaluating tactical options, analyzing topographic data, calculating force requirements for specific objectives, and designing optimal routes through military defenses. Historical data suggests that insurgents have utilized algorithmic models to right-size attacking units, reducing unnecessary personnel deployment while maximizing operational efficiency.
- Active Execution: Troubleshooting equipment malfunctions in the field, repairing communications hardware, adjusting drone release mechanisms, and calculating payload capacities for improvised aerial devices.
- Post-Operation Review: Deconstructing engagement outcomes, analyzing why specific tactical maneuvers succeeded or failed, and updating internal doctrine based on algorithmic synthesis of field reports.
This institutionalization creates structural durability. When individual fighters are captured or killed, the operational knowledge required to access and utilize artificial intelligence remains embedded within the faction's specialized units and standard operating procedures. The capability survives individual attrition.
Economic And Strategic Implications For State Actors
The integration of commercial technology into asymmetric warfare challenges traditional deterrence and counter-terrorism frameworks. For decades, state actors focused on physical interdiction: restricting precursor chemicals, monitoring communication channels, and disrupting physical supply chains. While these measures remain necessary, they are fundamentally incomplete when the cognitive tooling required for attacks exists in the digital cloud, accessible via standard consumer hardware.
The economic model of frontier AI exacerbates this challenge. The capital expenditure required to train these models is absorbed by major technology firms, while the marginal cost of inference approaches zero. Militant groups piggyback on corporate infrastructure funded by venture capital and enterprise contracts. They extract high-value technical synthesis without bearing any of the development costs.
This dynamic creates a severe strategic disadvantage for counter-terrorism agencies. Traditional intelligence operations rely on mapping human supply lines and financial transactions. When an insurgent group replaces a human expert with an LLM query, the traditional signal-to-noise ratio in intelligence gathering changes. A search query for chemical precursors leaves a different footprint than the physical procurement of those chemicals. Detecting intent requires monitoring digital interaction patterns at a scale that strains privacy laws and technical capabilities alike.
Furthermore, the involvement of transnational networks accelerates capability transfer. When foreign technical advisors provide hands-on training in prompt engineering and circumvention techniques, regional insurgent factions rapidly bridge the gap between crude traditional tactics and digitally optimized operations.
Systemic Vulnerabilities In Platform Governance
The root cause of this operational security failure lies in the underlying incentives of the technology sector. Commercial imperatives prioritize lower friction, broader accessibility, and rapid user acquisition. Every barrier introduced to stop malicious actors—such as stringent identity verification, mandatory phone number registration, or aggressive behavioural monitoring—also introduces friction for legitimate enterprise and consumer users.
Technology companies face a persistent trade-off between absolute safety and user experience. Because the vast majority of users are benign, platforms lean toward permissive architectures, relying on post-hoc moderation and iterative fine-tuning to patch vulnerabilities as they are discovered. For state-level actors or corporate competitors, this reactive posture is manageable. For well-funded, highly motivated terrorist organizations operating in regions with weak regulatory enforcement, this window of vulnerability is wide enough to exploit.
The proliferation of open-weights models compounds this structural flaw. Unlike proprietary APIs where providers can instantly revoke access or alter server-side filters, open-weights models can be downloaded, modified, and deployed locally on sovereign hardware with all safety filters permanently stripped. As open-source capabilities approach parity with proprietary frontier models, centralized platform moderation becomes increasingly irrelevant for determined adversaries.
Strategic Forecast And Structural Adjustments
Mitigating the risks of algorithmic weaponization requires abandoning the illusion that software safety filters can be made foolproof. As long as frontier models retain general-purpose reasoning and technical synthesis capabilities, adversarial optimization will find bypass vectors.
Effective counter-strategy must therefore shift from content filtering to behavioral anomaly detection and infrastructure-level attribution. Technology providers must implement runtime monitoring that identifies systematic patterns of dual-use prompting, regardless of how cleverly the prompt is disguised. This involves analyzing request velocity, multi-turn conversational trajectories designed to elicit restricted knowledge, and infrastructural fingerprints associated with proxy evasion.
Simultaneously, security agencies and intelligence frameworks must treat algorithmic tools as active participants in the threat matrix. Just as financial institutions are mandated to monitor transactions for money laundering signals, cloud and AI providers must operate under strict regulatory frameworks that mandate the reporting of systemic, high-risk technical inquiries associated with explosive manufacturing and CBRN vectors.
The convergence of militant insurgency and commercial artificial intelligence has permanently altered the threat landscape. The assumption that advanced technological capabilities require state-level resources is obsolete. Without a fundamental restructuring of how software providers audit access and police adversarial interaction, the quiet institutionalization of frontier intelligence by non-state actors will continue to accelerate, shifting the balance of asymmetric conflict toward those willing to exploit every loophole in the digital commons.